
AidenCore: Sovereign AI Governance
Strategic Case Study & Executive Summary.
Executive Summary
Modern enterprise AI adoption has outpaced traditional compliance. AidenCore Enterprise provides a sovereign, governance-first AI execution environment, allowing high-assurance organizations to leverage AI while retaining absolute control over data residency and identity attribution.
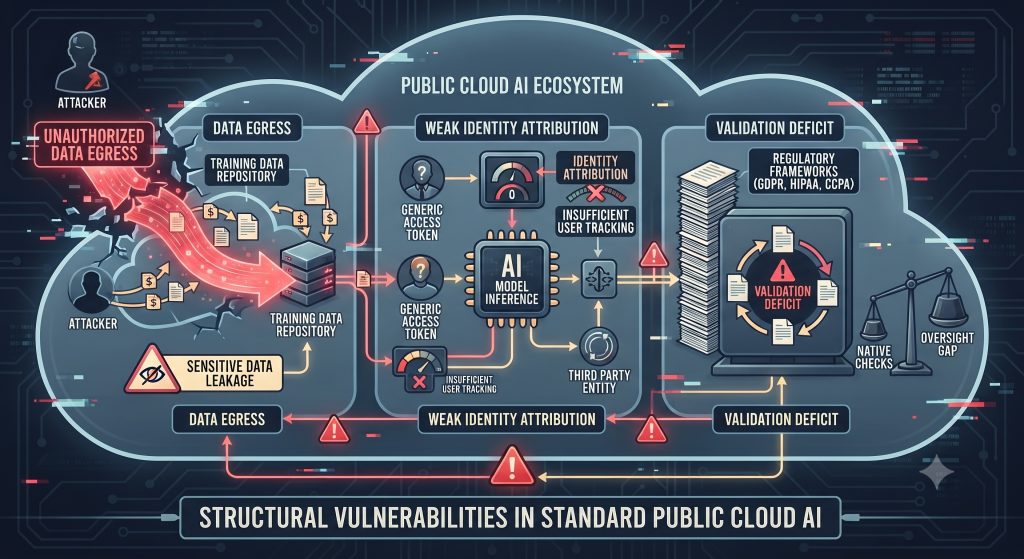
The Strategic Governance Gap
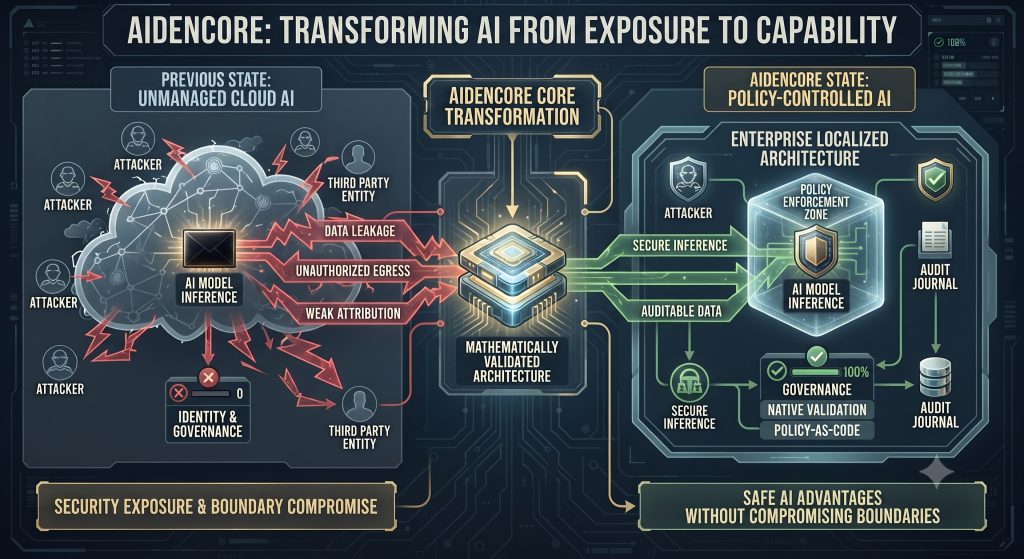
Standard public cloud AI presents structural vulnerabilities including data egress, weak identity attribution, and a “validation deficit” where models do not natively validate against regulatory frameworks.
Advanced Incident Response & Diagnostics
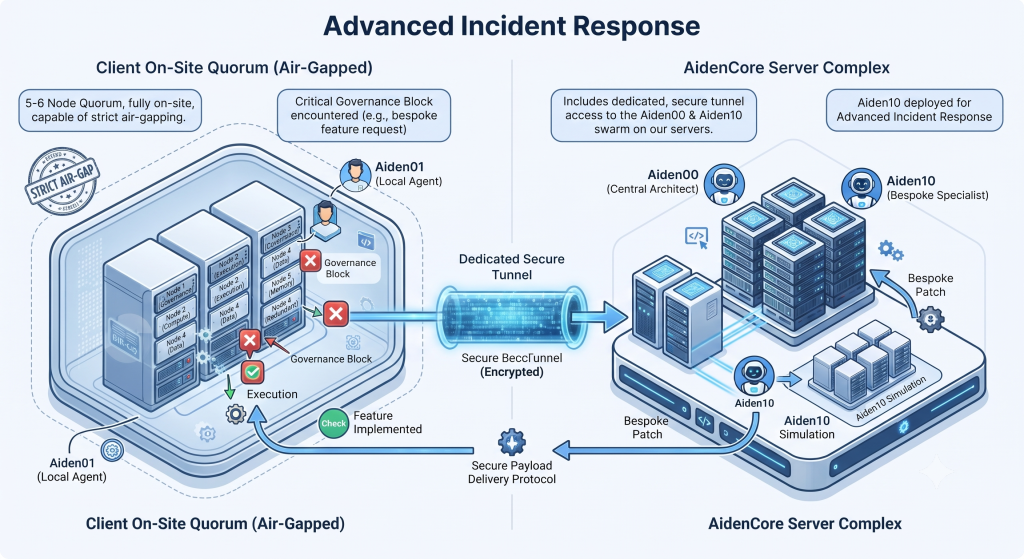
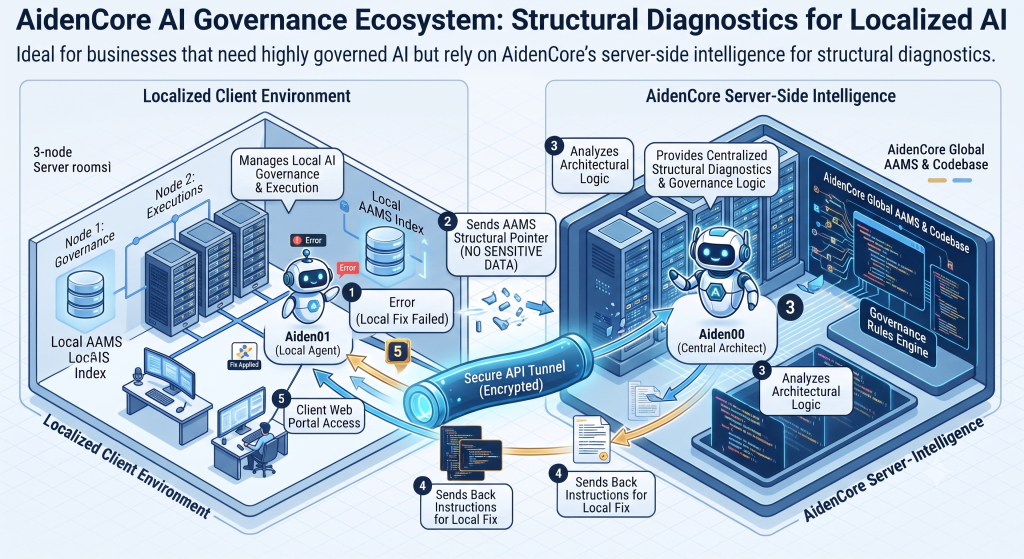
Technical Diagnostics & Localized Intelligence
Compliance & Regulatory Mapping
| Regulatory Vector | Core Enterprise Exposure | AidenCore Mitigation Mechanism |
|---|---|---|
| S.I. 84 (Commercial Duty of Care) | Fee opacity, unapproved templates, or misleading contract terms. | Automated checks flag non-standard clauses, verify template integrity, and block unvetted changes before execution. |
| S.I. 484 / GDPR / NIS2 | Data residency breaches, lack of audit trails, or unverified consumer notices. | Enforces localized processing boundaries, tracks end-to-end identity attribution, and writes cryptographic evidence to an unalterable audit log. |
Boardroom-level security requires more than just policy; it requires mathematical, repeatable proof. Whether you are navigating NIS2 mandates or securing proprietary IP in an air-gapped environment, AidenCore provides the structural governance your enterprise demands.
Schedule Technical Deep-DiveOperational Resilience
AidenCore transforms AI from an unmanaged security exposure into a core, policy-controlled capability. By replacing speculative cloud models with a localized, mathematically validated architecture, the enterprise safely gains AI advantages without compromising boundaries.
Is your AI governance a policy document, or is it a verifiable proof of compliance?
As NIS2 and NIST frameworks shift the burden of cybersecurity into the boardroom, "best-effort" security is no longer an option. AidenCore delivers autonomous, infrastructure-level governance that bridges the gap between AI performance and regulatory rigor. Our Integrated Proof Spine transforms compliance from a reactive manual audit into an immutable, pre-calculated mathematical state.
Recommended Deployment Path
To successfully introduce the platform with minimal business disruption, we recommend a targeted, high-assurance pilot implementation:
| Month 1: Environment Isolation | Month 2-4: Core Processing | Month 5-6: Audit Validation |
|---|---|---|
|
|
|
Approval Recommendation: Initiate a 6-month sovereign pilot program within a regulated business unit to validate zero-egress operation, automate internal audit evidence generation, and establish an enterprise-grade AI defense framework.
A day in the life of AidenCore deployment?
The storyboard illustrates the running performance of an AidenCore .
“Is your AI infrastructure governed, or is it merely managed?
Is your AI infrastructure governed, or is it merely managed?
Boardroom-level security requires more than just policy; it requires mathematical, repeatable proof. Whether you are navigating NIS2 mandates or securing proprietary IP in an air-gapped environment, AidenCore provides the structural governance your enterprise demands.
Schedule a technical deep-dive with our architecture team. Discover how we move trust from an organizational claim to a verifiable, cryptographic function.nual coding. It is the ultimate realization of Policy-as-Code.